Controlled AI. Real results.
Wrap existing tools with governed orchestration
Many teams already own the tools. Arqent adds the missing layer: policy-aware routing, execution logs, evidence capture and workflow packaging.
Product view
Put policy, evidence and repeatability around every tool call
Arqent turns existing APIs, MCP servers, data sources and internal services into governed tools that run inside the case context.
Inventory
APIs, MCP servers, vendors and internal services
Policy
Role, case, classification and approval routing
Execution
Logged tool calls and captured outputs
Package
Repeatable workflow or deployable Solution
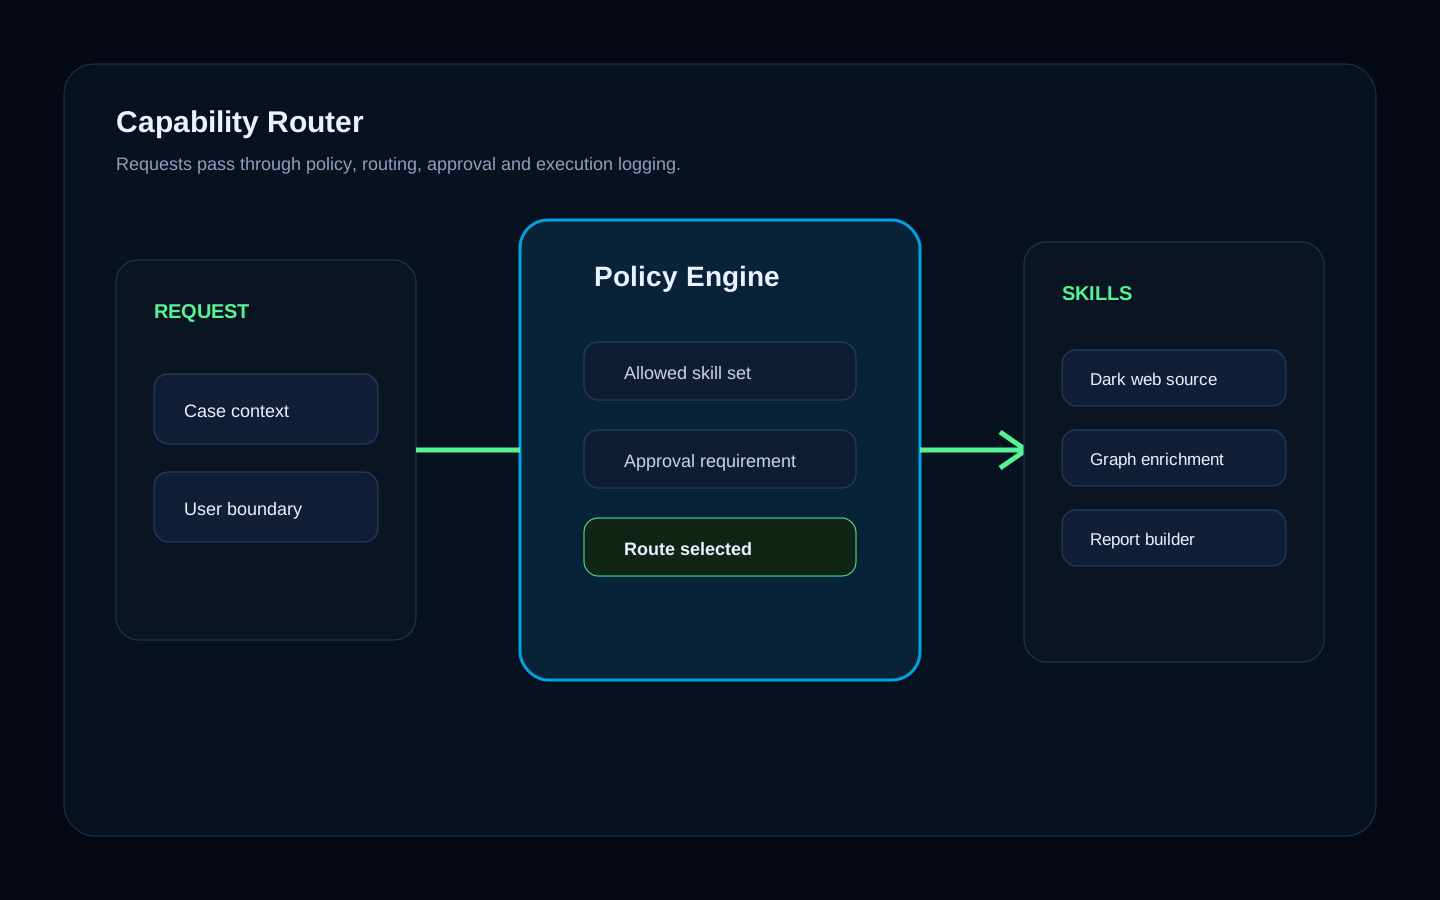
TOOL GOVERNANCE
Every tool call passes a policy first
What platform teams get back
Use what already works
Wrap existing tools instead of replacing every source, vendor or internal service.
Govern execution
Decide who can run which capability, in which case and under which approval path.
Capture evidence
Preserve tool outputs, logs, artifacts and reports with the case.
Ship repeatable workflows
Package common toolchains into controlled workflows or customer-ready Solutions.
Where tool orchestration usually breaks
Most regulated teams already have tools. What they lack is a controlled layer that knows which tool can run, why it is allowed and where the output belongs.
Arqent provides that orchestration layer. Requests pass through policy, tools run under governance and the output stays tied to evidence, review and workflow packaging.
WHAT EXISTS
Tool inventory
Identify APIs, MCP servers, data sources and internal services that can become governed tools.
WHAT CAN RUN
Policy route
Route execution by case, role, classification, approval and deployment requirements.
WHAT REMAINS
Evidence capture
Preserve tool outputs, logs and generated artifacts inside the case.
WHAT REPEATS
Packaged workflow
Turn repeatable operations into governed workflows or deployable Solutions.
Use cases
Tool orchestration workflow
Use this pattern when existing tools need governance, evidence capture and repeatable operating paths.
Platform teams
External tool orchestration
Your team already owns tools and data sources. Arqent wraps them as governed tools: a policy check before every call, a full execution history and results that land in the case.
Explore workflowSystems and sources
What the operator does
Results
Product view
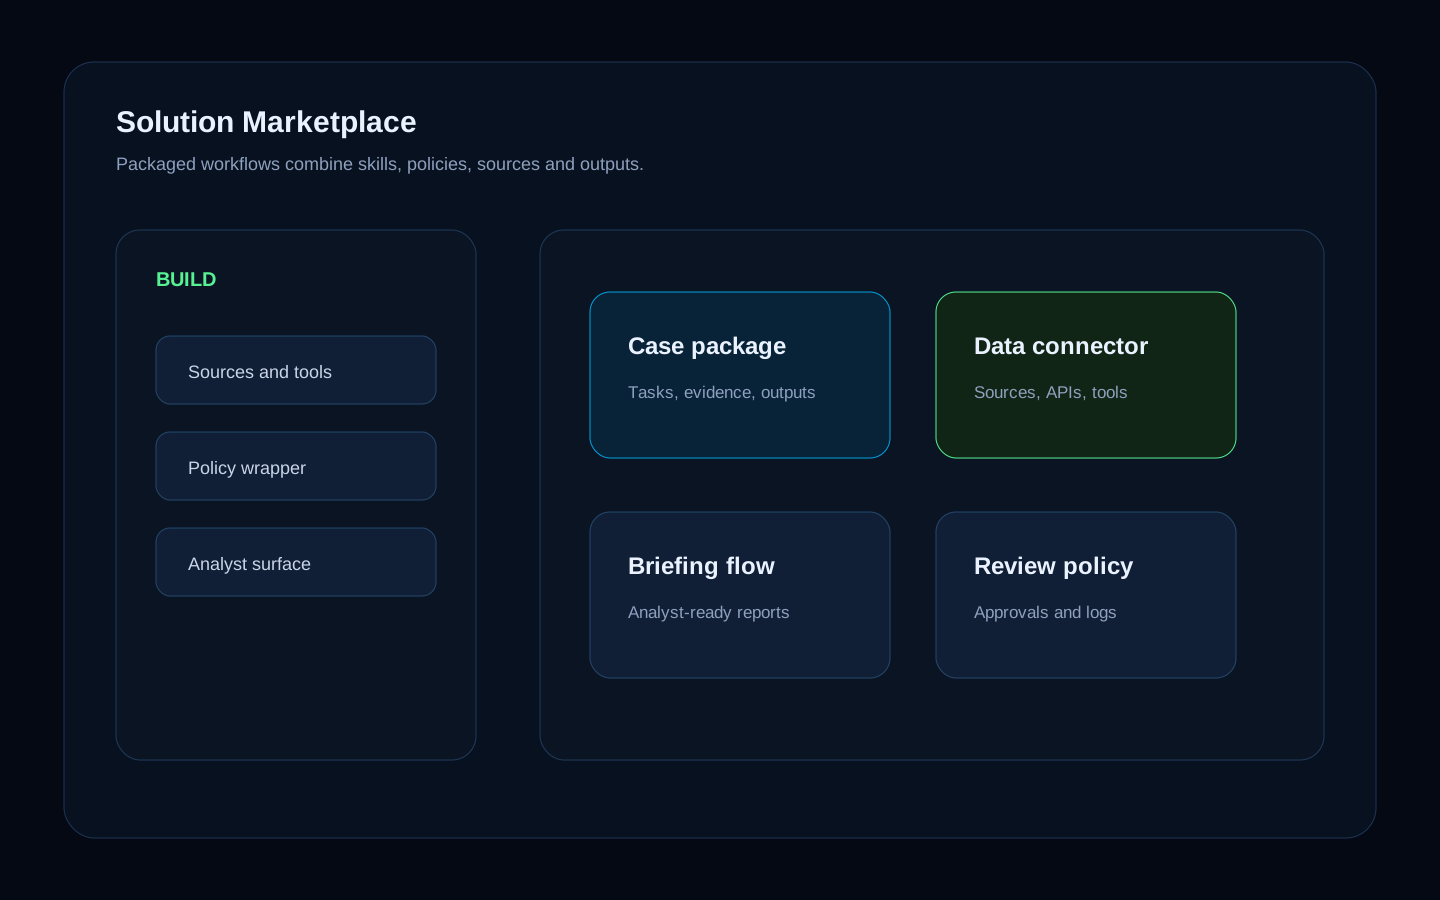
Turn governed toolchains into packaged Solutions
Once a toolchain is governed, it can become a repeatable workflow with buyer trigger, intake, controls, outputs and deployment assumptions.
Build
Tools, dashboards and data flows
Govern
Policies, approvals and audit logs
Package
Workflow metadata and expected outputs
Deploy
SaaS, on-premises or airgapped
SOLUTIONS
Capabilities become installable solutions
Trust model
Built for controlled capability routing
External orchestration needs clear authority, auditability and output control before automation scales.
Capability policy
Define what can run and under which conditions.
- Role checks
- Case checks
- Approval gates
Execution logging
Keep tool activity reviewable and replayable where appropriate.
- Tool logs
- Outputs
- Replay path
Evidence capture
Attach results to the case or packaged workflow.
- Artifacts
- Reports
- Decision context
Deployment control
Respect environment-specific tool and data boundaries.
- Network boundary
- Data policy
- Customer environment
Map your existing toolchain
Bring the tools, APIs and workflows you want governed under Arqent.