Controlled AI. Real results.
Turn suspicious email into reviewable evidence
Email forensics workflows need technical enrichment, correlation and a report that a reviewer can stand behind.
Product view
Turn a suspicious email into a defensible case record
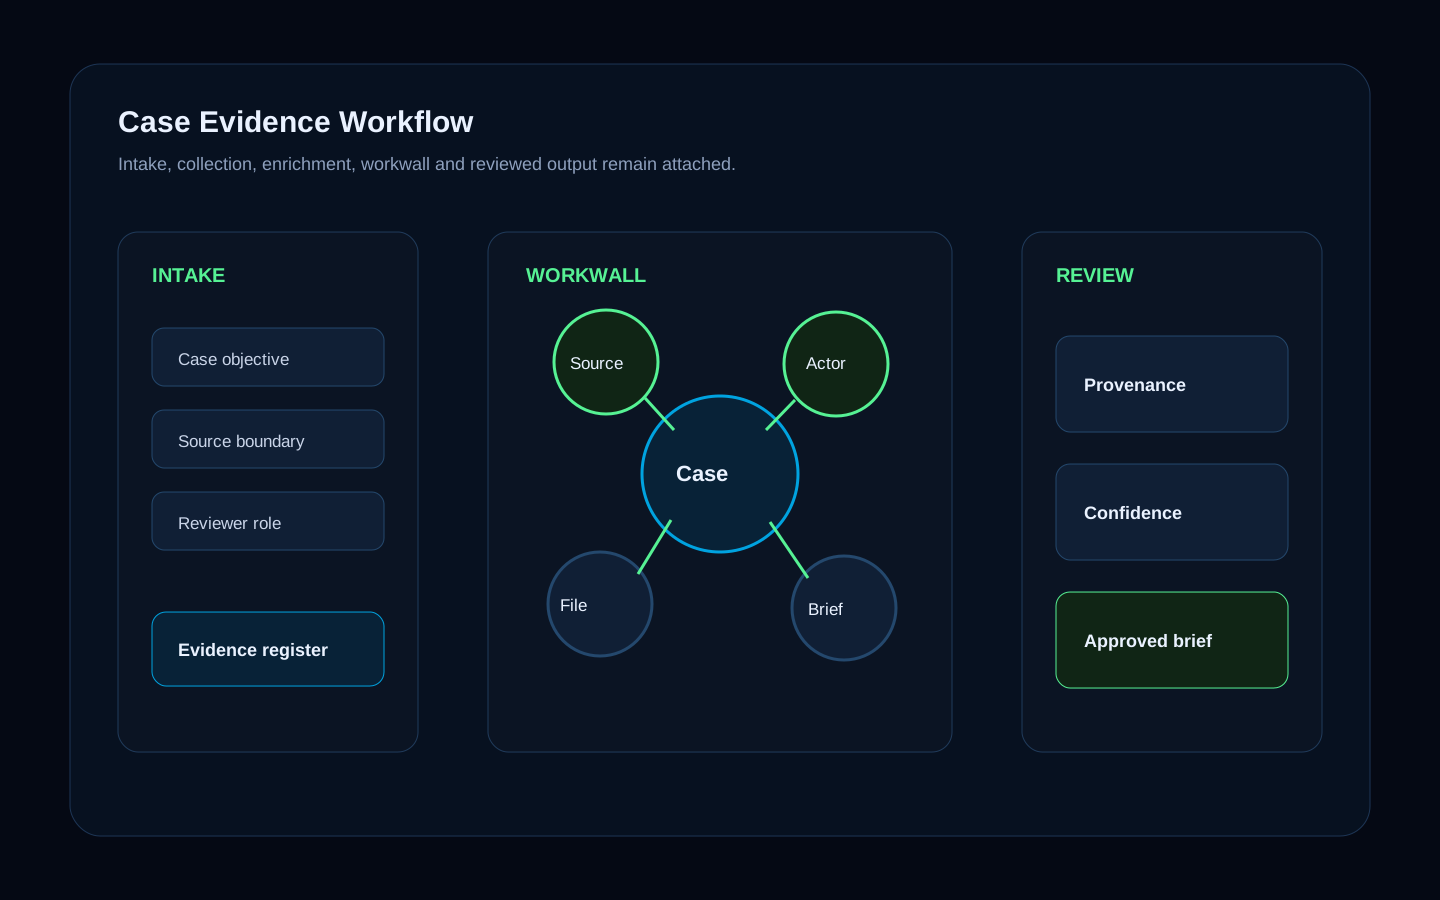
Arqent keeps the EML, headers, links, attachments, enrichment results, analyst notes and reviewer report attached to the same fraud or DFIR workflow.
Source
EML, headers, links and attachments
Enrichment
Domain, URL, identity and attachment checks
Correlation
Related accounts, wallets, domains and source notes
Report
Reviewer-ready findings and decision trail
EVIDENCE TRAIL
Every result stays linked to its sources
What fraud and DFIR teams get back
Faster first pass
Move from suspicious email to structured findings without rebuilding context across tools.
Preserved artifact context
Keep the source file, metadata and enrichment outputs available for review.
Connected indicators
Link domains, accounts, wallets, dark web references and other case entities when relevant.
Reviewer confidence
Show what was checked, what remains uncertain and why the output supports escalation or closure.
Where email triage usually breaks
BEC and suspicious-email work starts with one artifact, then fans out into headers, domains, links, attachments, account context and analyst notes.
Arqent keeps those checks inside one case workflow. The result is not just an answer; it is a reviewable record of the artifact, enrichment, reasoning and output.
EML CONTEXT
Source file
Preserve the source artifact and relevant metadata inside the case.
INDICATORS
Technical enrichment
Headers, domains, links and attachments can be routed through governed tools.
RELATIONS
Correlation
Connect email findings with domains, accounts, wallets or dark web references where relevant.
OUTPUT
Reviewer report
Produce a reviewable report with evidence artifacts and decision trail.
Use cases
Email forensics workflow
Use this pattern when a suspicious email needs technical enrichment and reviewer-ready evidence, not a disconnected lookup chain.
Fraud and DFIR
Email forensics and BEC
A suspicious email is analysed – headers, domains, links and attachments – enriched, correlated with the case and turned into a report a reviewer can stand behind.
Explore workflowSystems and sources
What the operator does
Results
Product view
Connect email indicators to wider case context
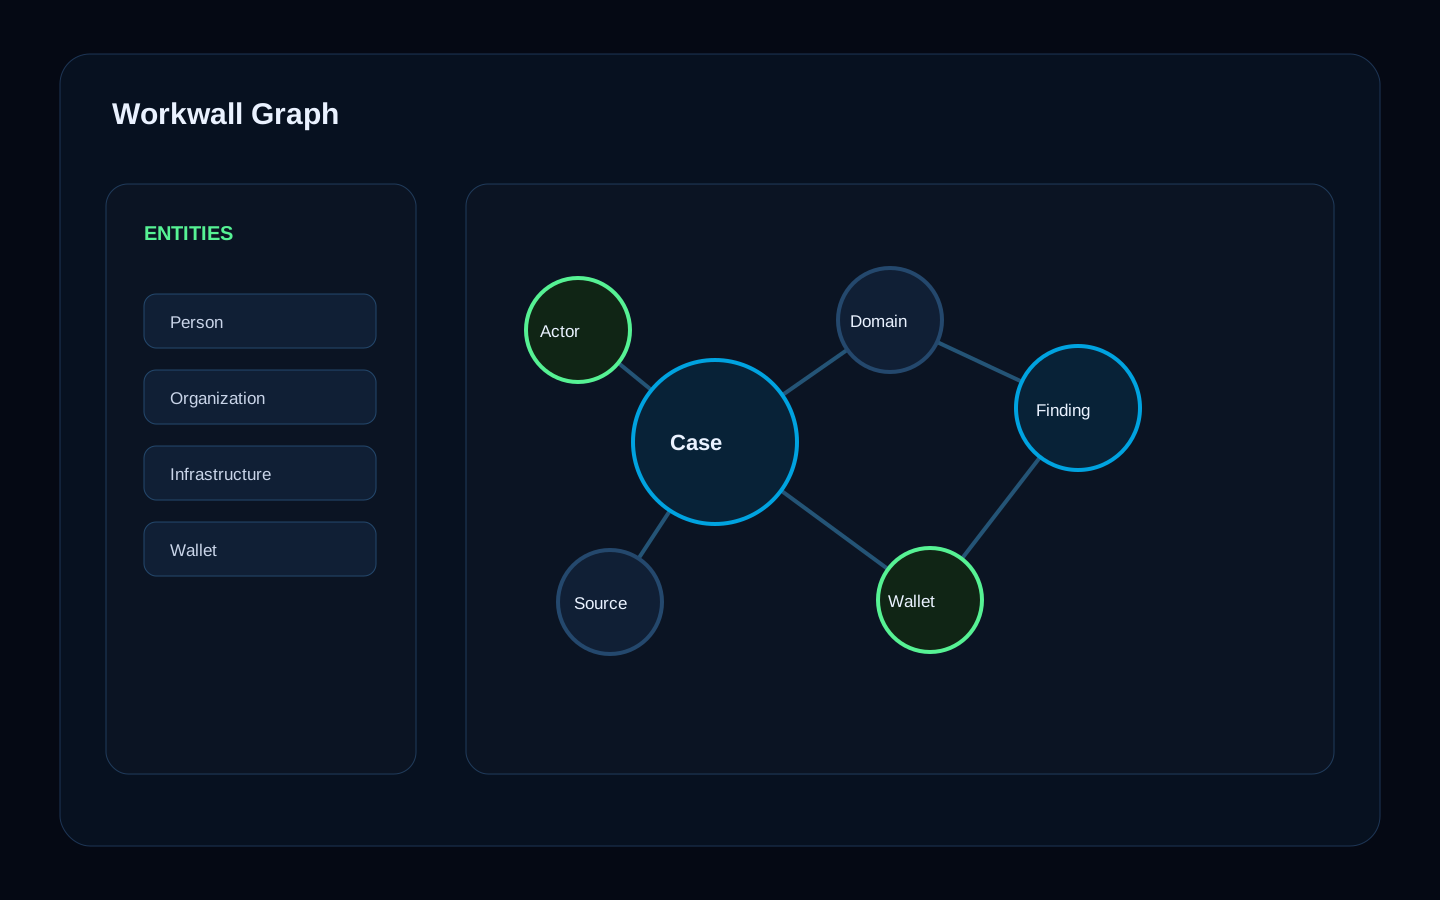
Domains, sender accounts, URLs, attachments, wallet references and actor notes can become connected findings before the report is written.
Indicators
Headers, domains, URLs, accounts and attachments
Context
Related cases, source notes and enrichment outputs
Relations
Why an indicator changes the assessment
Decision
Escalate, monitor, close or brief
CASE GRAPH
Findings become connected context
Trust model
Built for reviewable forensic work
Email forensics needs speed, but the artifact trail and reviewer context cannot disappear.
Artifact integrity
Preserve the source email and relevant metadata.
- EML context
- Metadata
- Attachment notes
Tool transparency
Keep enrichment outputs tied to the case.
- Domain checks
- URL checks
- Execution log
False-positive control
Keep uncertainty visible before escalation.
- Confidence notes
- Reviewer checks
- Limits
Report readiness
Produce outputs a reviewer can understand and defend.
- Findings
- Decision trail
- Export context
Map an email forensics workflow
Start with source artifacts, enrichment expectations and reviewer output requirements.